v2.0 Release — MIT · no warranty · v2.0.0 · Disclaimer
Star on GitHub →
FULLY LOCAL • ZERO CLOUD

Your logs.
Your LLM.
Real security.

RocketLogAI v2 is a local-first security platform for homelabs and learning — syslog monitoring, unified AI brain, guarded remediation, WAF/AV shield, and mobile API. Uses your own offline LLM and keeps every byte on your hardware. Hobby software — provided AS IS. Read the disclaimer.

Start in 60 seconds → See it in action
Docker • Python • One binary feel
•
v2.0.0 Ecosystem • MIT • Architecture
🏠 Home Assistant power users
🔒 Air-gapped & offline environments
🖥️ Homelab & small IT teams
🏭 Industrial / legacy systems (IBM i)
PRIVACY
100%
local. Your data never leaves the machine. No telemetry, no phoning home.
LLM
Your model
LM Studio, Ollama, vLLM, or Azure/M365 Copilot. Structured JSON analysis.
INTEGRATIONS
Deep HA
Device registry, rich alerts, sensors, events. Forward logs from all addons.
SAFETY
Guarded
Remediation is disabled by default. Multiple layers: dry-run, confirmation, allow-lists.
v2 ECOSYSTEM

Four products. One unified AI brain.

🚀
RocketLogAI
Core syslog, threat detection, AI assistant, devices, daily briefing, config.
🔧
RocketRemediate
Dry-run remediation, approval workflow, backups, rollback orchestration.
🛡️
RocketShield
WAF + AV on decrypted traffic, parental controls. Inline or SPAN mode.
📱
RocketAI Mobile
iOS/Android/TV API — QR pairing, local-first sync, remote PC/Mac control.
Shared: MCP server · Vector RAG · UEBA · Audit logging · Prometheus metrics · Zero Trust RBAC
CAPABILITIES

Everything a local SIEM should be.

🧠
Local LLM Analysis
Rule engine first, then high-value logs go to your model for context-aware threat detection, summaries, and suggested fixes. Excellent with Qwen2.5, Llama 3.1/3.3, Command-R.
🏠
Home Assistant Superpowers
Pulls your actual device registry. Matches IPs/MACs to lights, sensors, switches. Fires notifications, events, updates sensors. Forward all addon + core + supervisor logs via the syslog addon.
💓
Active Heartbeat Monitoring
Not just "is the port open?". Verifies the *right* website version, SSH config up to date, services healthy. Failed or stale heartbeats become first-class threats that go through the full analysis pipeline.
📅
Daily Briefing (Operator Companion)
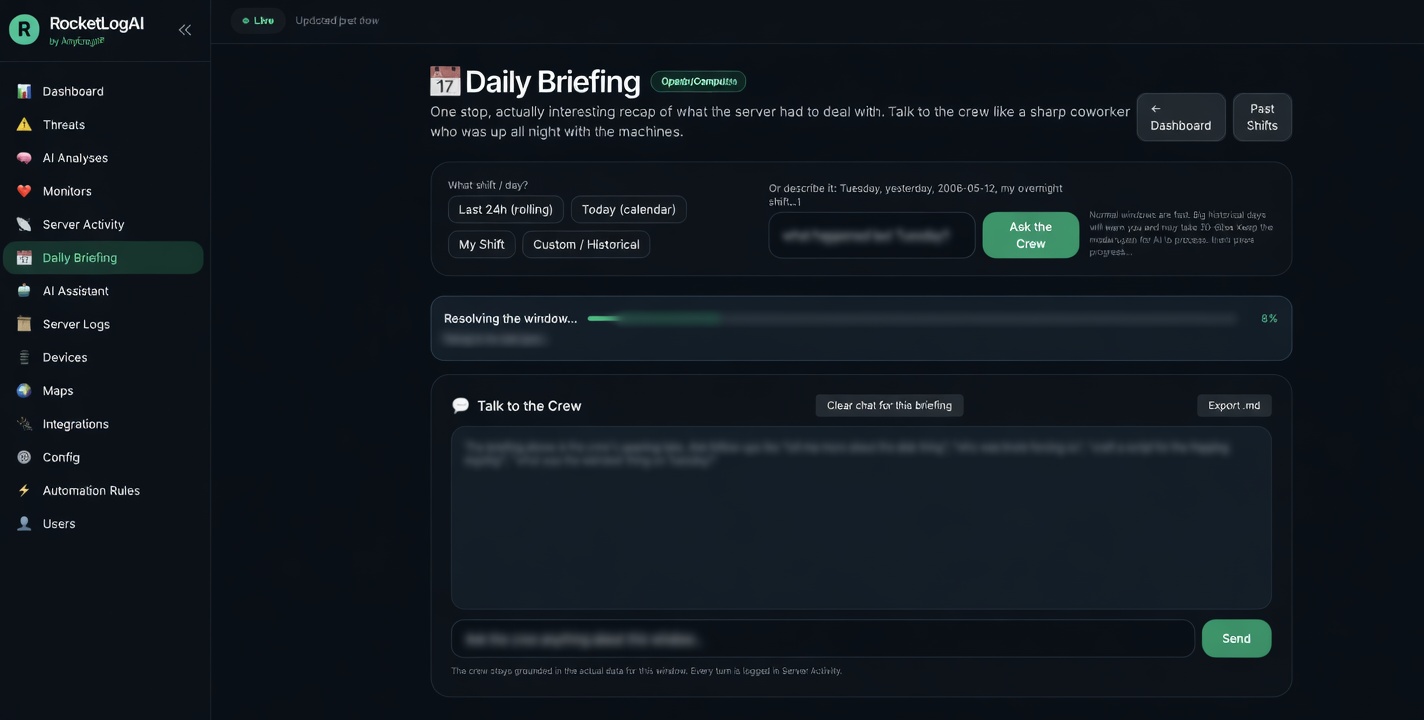
Entertaining, grounded recap of the day/shift. Chat naturally: "why the spike at 3am?", "draft a fix script", "promote this to a standing monitor". Full history persisted.
🤖
Built-in AI Assistant
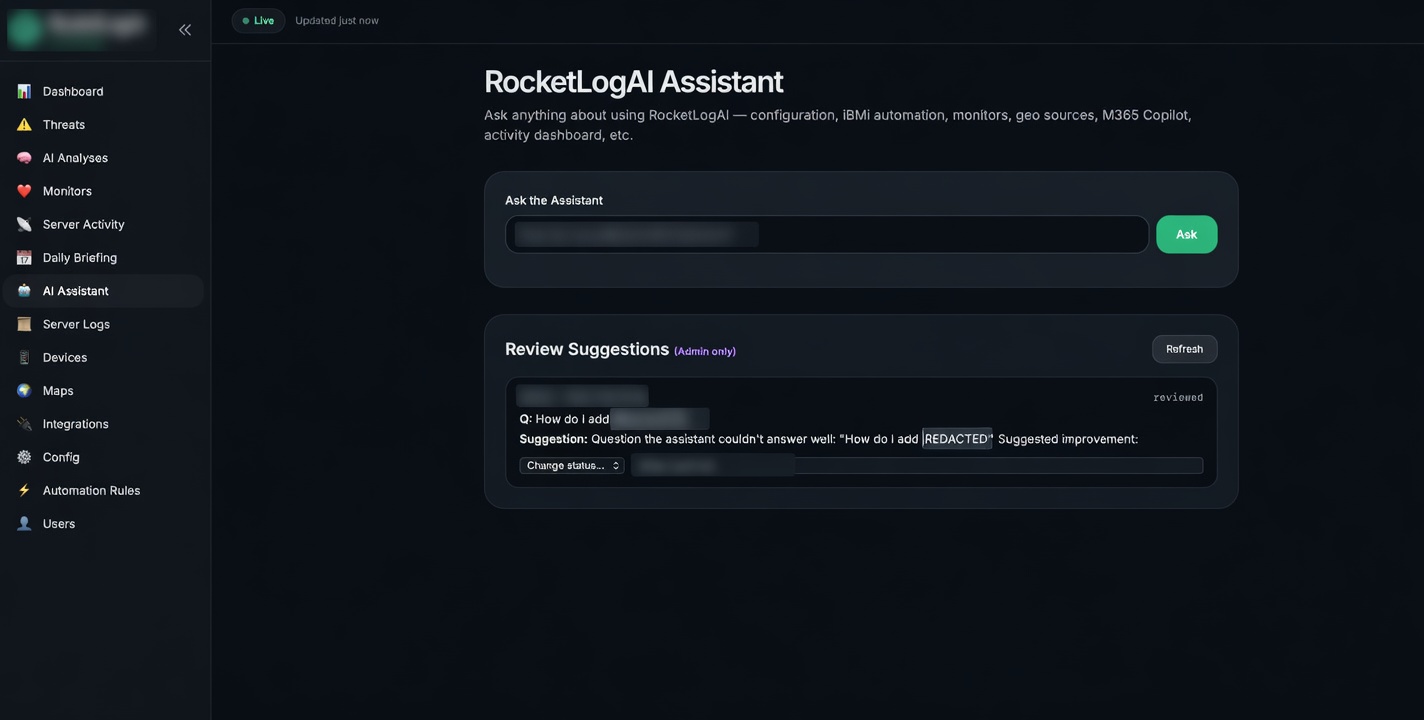
Ask about config, iBMi automation, monitors, anything. Self-documenting. Submit feature suggestions through the UI — admins review them in the same place.
🗺️
Offline + Multi-Source Geo
Free MaxMind GeoLite2 (city level) + optional paid providers merged with priority. Every threat gets location without leaking IPs to third parties.
🛠️
Guarded Remediation & Monitors
Huge library of prebuilt remediation scripts (Linux, Windows, Cisco, Ubiquiti, pfSense, IBM i, cert renewal, etc.). English → safe script generator. All actions require explicit enable + confirmation.
🔌
Broad Log Sources
Syslog UDP/TCP (real 514 or 5140), network gear, Linux rsyslog, Windows (NXLog etc), HA addons, Docker logs, custom apps. RFC3164 + 5424 + best-effort.
🛡️
Fast Deterministic Rules + MAC + Blacklists
Built-in high-value patterns for brute force, sudo abuse, crypto miners, kernel panics, etc. + custom patterns. MAC vendor lookup (IEEE + Wireshark manuf) + learned device behavior profiles.
🔗
Unified AI Brain + MCP
Vector RAG memory shared across all products. MCP server for Claude Desktop, Cursor, etc. Run logsentinel mcp on stdio.
📊
UEBA + Explainable Reports
Behavioral anomaly detection with human-readable explanations. Organization tasks with AI-assisted remediation on the dashboard.
🔐
Enterprise Auth & Audit
AD/LDAP + Entra ID OAuth. Four-tier RBAC. Full audit trail. Prometheus metrics at /api/v2/metrics.
PIPELINE

Simple. Powerful. Transparent.

01
Ingest
Syslog UDP/TCP listeners. Parse RFC3164/5424. Store in SQLite with retention.
02
Rule Engine
Fast deterministic patterns + severity scoring. Immediate threat records for matches.
03
LLM Analysis
Periodic batches of interesting logs sent to *your* local model. Structured JSON: summary, severity, recommended action, IOCs.
04
Enrich & Alert
Geo (offline), device intel (HA + MAC), heartbeats, blacklists. Webhooks + rich HA notifications.
05
Act (optional)
Human-in-the-loop confirmation before any remediation. Full audit trail. Promote good fixes to monitors.
Everything stays on your box. The only "AI" calls are to the LLM endpoint *you* configured (localhost:1234 by default).
PLAYGROUND
Try the analysis engine
client-side simulation

Paste a realistic syslog line (or click an example). This runs the same style of rule engine + structured output that the real local LLM produces in RocketLogAI. A taste of what your instance will show on /threats and in the Daily Briefing.

THE EXPERIENCE

A dashboard you'll actually enjoy using.

Fast, calm, information-dense. Built with the same attention to detail as the analysis engine.
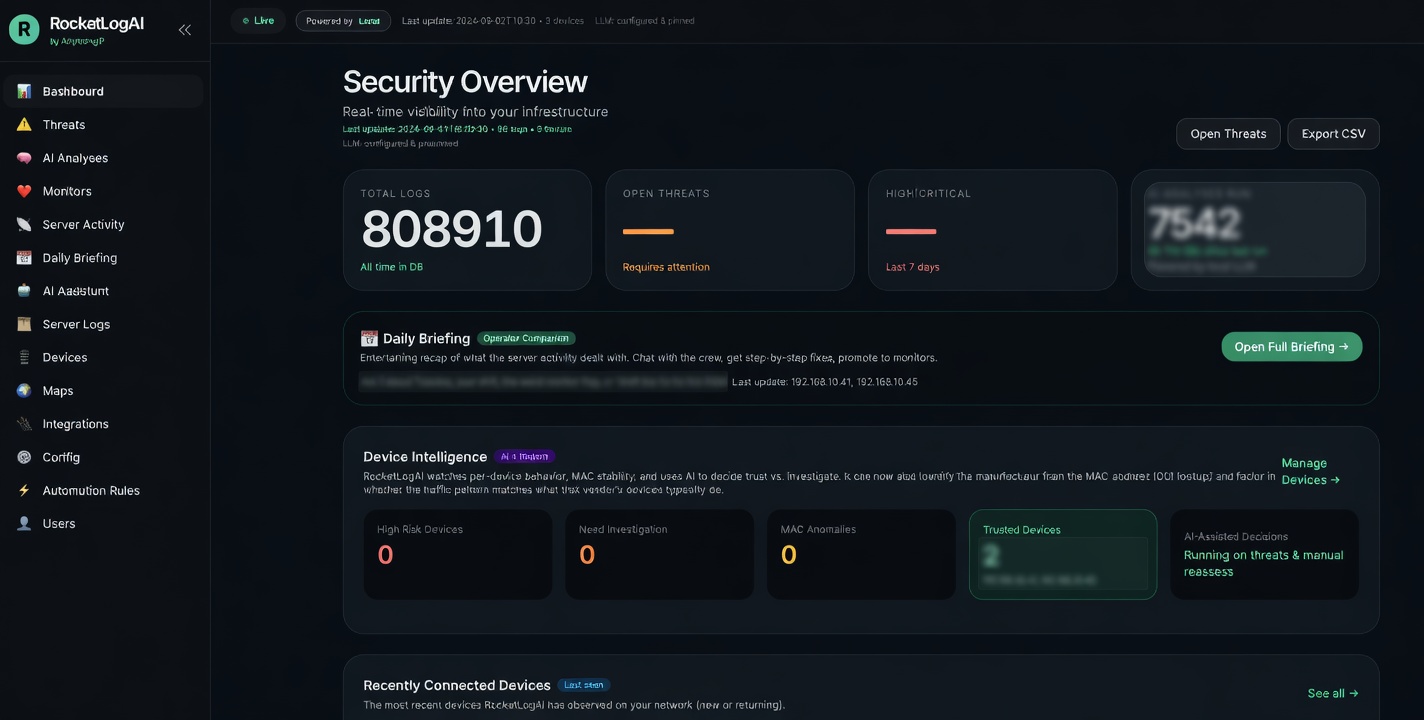
RocketLogAI main dashboard with large metrics for total logs, open threats, high/critical, AI analyses, plus Daily Briefing teaser and Device Intelligence cards
Dashboard Real-time overview
Live metrics, open threats, AI usage, trusted devices, and the Daily Briefing entry point.
RocketLogAI Daily Briefing page showing an entertaining recap of the day's logs and threats with chat interface for asking follow-up questions
Daily Briefing Operator Companion
Entertaining shift recap. Chat naturally: “what spiked at 3am?”, “draft a fix script”, promote to monitors.
RocketLogAI built-in AI Assistant chat interface for asking about configuration, automation, iBMi, and submitting feature suggestions
AI Assistant Self-documenting
Ask anything about the tool or your environment. Submit suggestions that admins can review in the same UI.
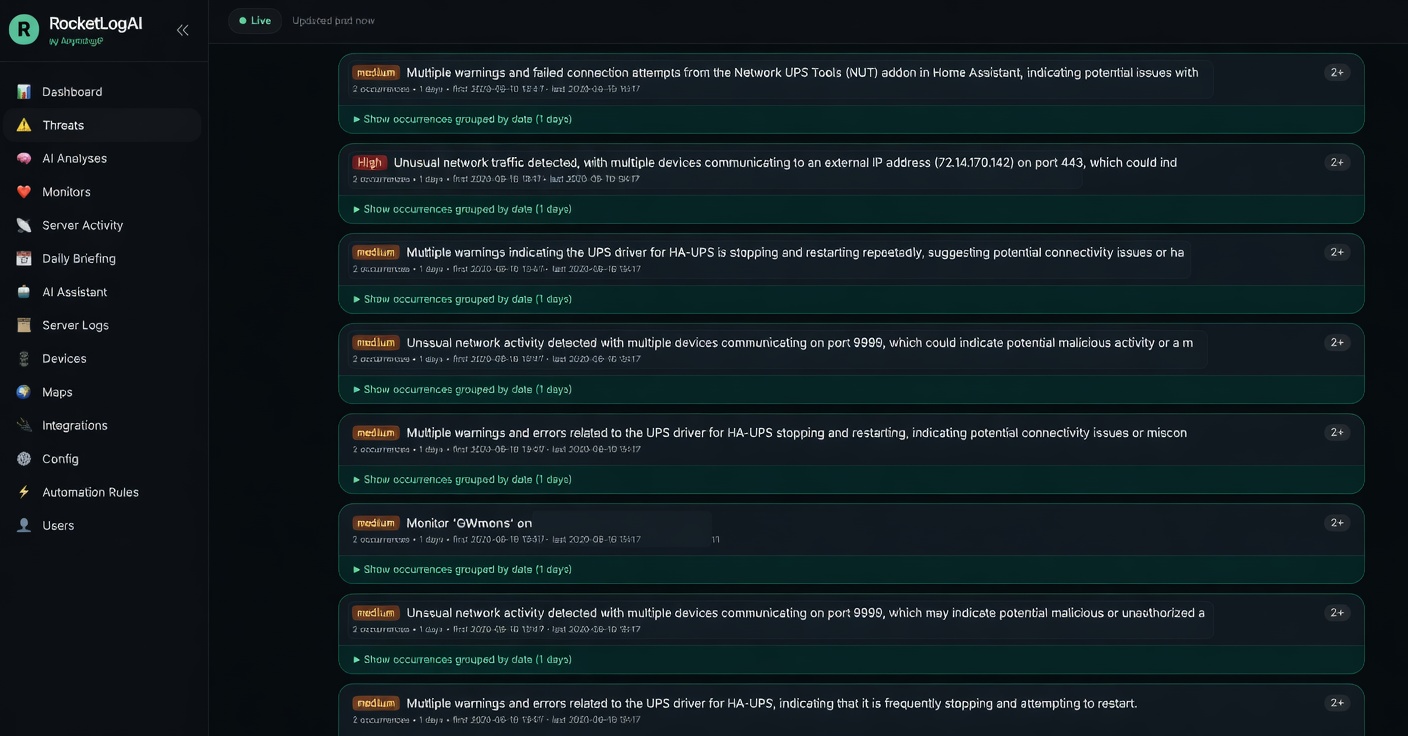
RocketLogAI Threats view listing detected issues with source/destination IPs, ports, geo location, severity, and linked device names from Home Assistant or learned profiles
Threats With full context
Per-occurrence IPs/ports, geo enrichment, device names (e.g. “Bedroom Camera”), rule + LLM reasons.
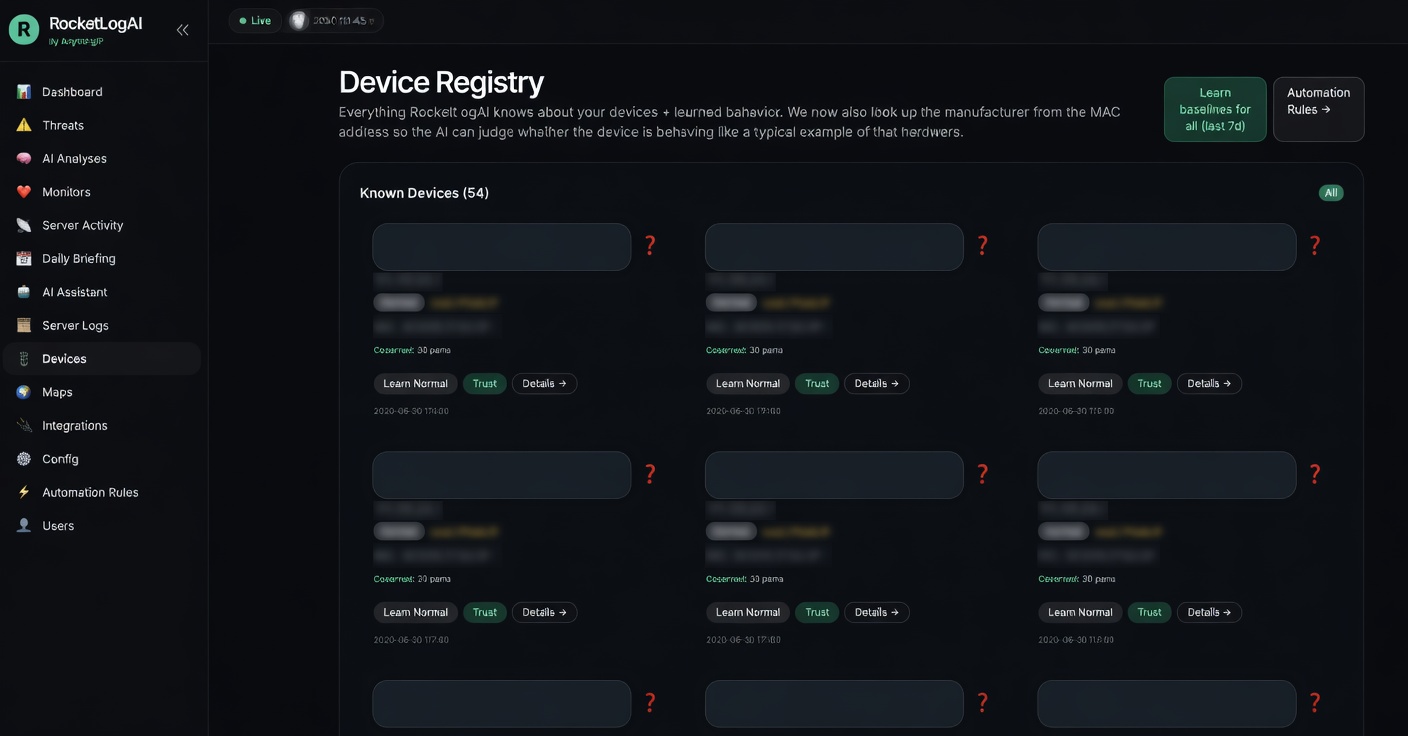
RocketLogAI Device Intelligence and detail view showing behavior history, MAC vendor, geo sources, port hygiene, and trust scoring
Device Intelligence MAC + HA + behavior
Learned profiles, manufacturer lookup (IEEE + Wireshark), Home Assistant device mapping, and hygiene signals.
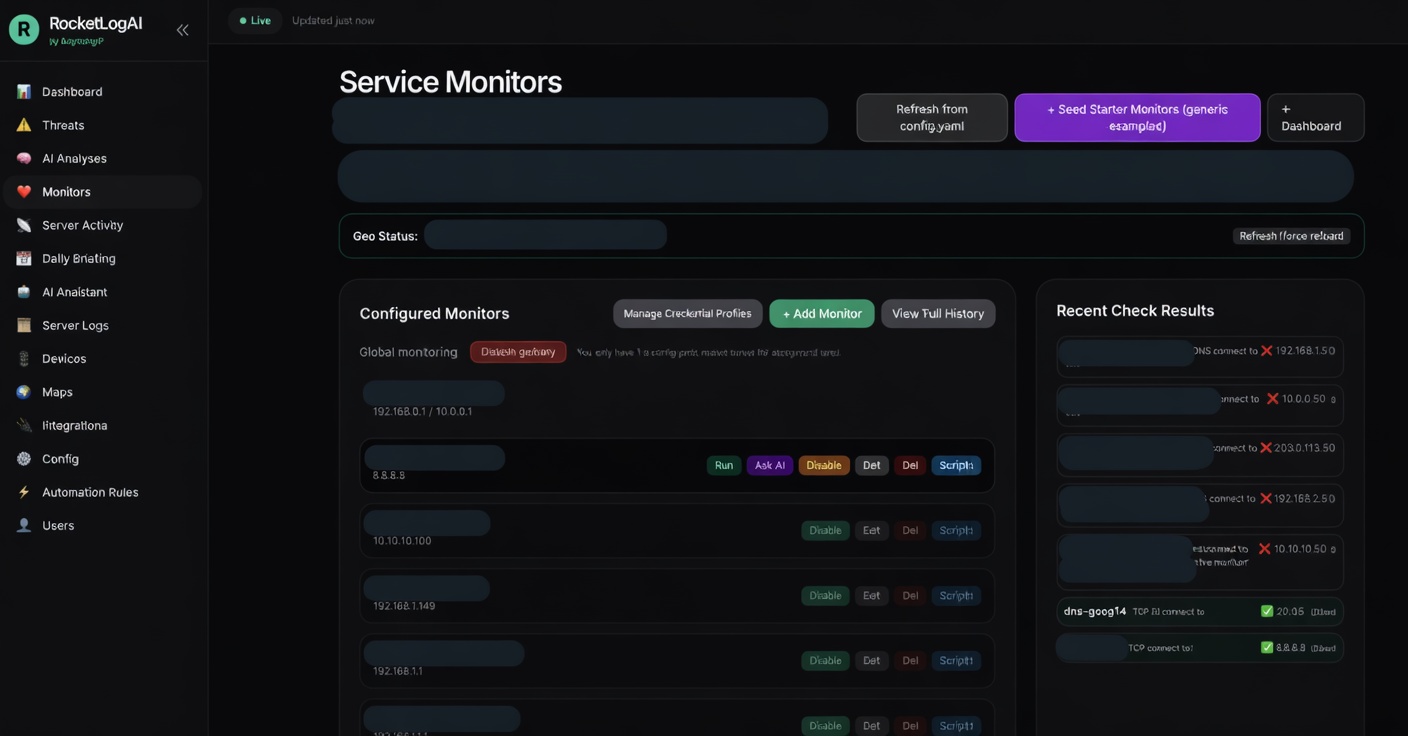
RocketLogAI Monitors and Automation page with English-to-script generation, credential profiles, and recent probe results
Monitors & Automation Guarded actions
Service monitors, heartbeat checks, prompt → safe remediation script generator, and human-approval flows.

Real screenshots from a live instance (with sensitive IPs/hostnames redacted for public sharing). Captured from the actual RocketLogAI UI at port 8787.

The images are now using the clean redacted versions. Originals with full details remain in the folder if you ever need them.
THE PHILOSOPHY
Most "SIEM + AI" products phone home or require expensive licenses.
RocketLogAI is the opposite.

Everything runs on your machine, against your local model, with full transparency and strong safety rails around any automated response.

From AnythingIP — built for people who want control.
RocketLogAI — local AI-powered log security
OPEN SOURCE
Built in public. For everyone.

The full v2 source — Python core, FastAPI web UI, unified AI brain, RocketRemediate, RocketShield, mobile API, Helm chart, CI/tests, installers — is on GitHub under the MIT license.

Contributions welcome: new parsers, custom rules, more remediation scripts, better prompts, Windows Event Log support, docs, or anything else that makes local log intelligence better.

Star on GitHub Open an issue or suggestion
Fork • Improve rules • Add integrations • Share remediation scripts
5 MINUTES TO FIRST THREAT

Get started

RECOMMENDED Docker Compose (easiest)
git clone https://github.com/AnythingIP/RocketLogAI.git
cd RocketLogAI
cp example-config.yaml config.yaml
# Edit config.yaml — at minimum set llm.base_url
#   LM Studio: http://host.docker.internal:1234/v1   (or your LAN IP)
#   Ollama:    http://host.docker.internal:11434/v1
docker compose up -d --build
# Open http://your-server:8787   (default login: admin / admin — change it!)
Download v2.0.0 release · one-click Linux installer with systemd · Helm chart included.
Native (Python)
git clone https://github.com/AnythingIP/RocketLogAI.git
cd RocketLogAI
pip install -e ".[web,v2,ai]"
logsentinel example-config -o config.yaml
# edit llm.base_url in config.yaml
logsentinel run --web
# or for real syslog port 514: sudo logsentinel run
Also ships one-click installers for Linux (systemd) and Windows (NSSM / scheduled task).
Need a local LLM? LM Studio or Ollama — load a good model (Qwen2.5 14B+ recommended) and point RocketLogAI at it.
© AnythingIP • MIT licensed · provided AS IS, no warranty.
Hobby/educational software — you are responsible for how you deploy it.
Developed with assistance from Grok Build / xAI. Not affiliated with xAI.